 Hawkcrest
🚧 Cloud for OT: Start with Non-Critical, Prove Value, Scale Securely
Originally published on LinkedIn
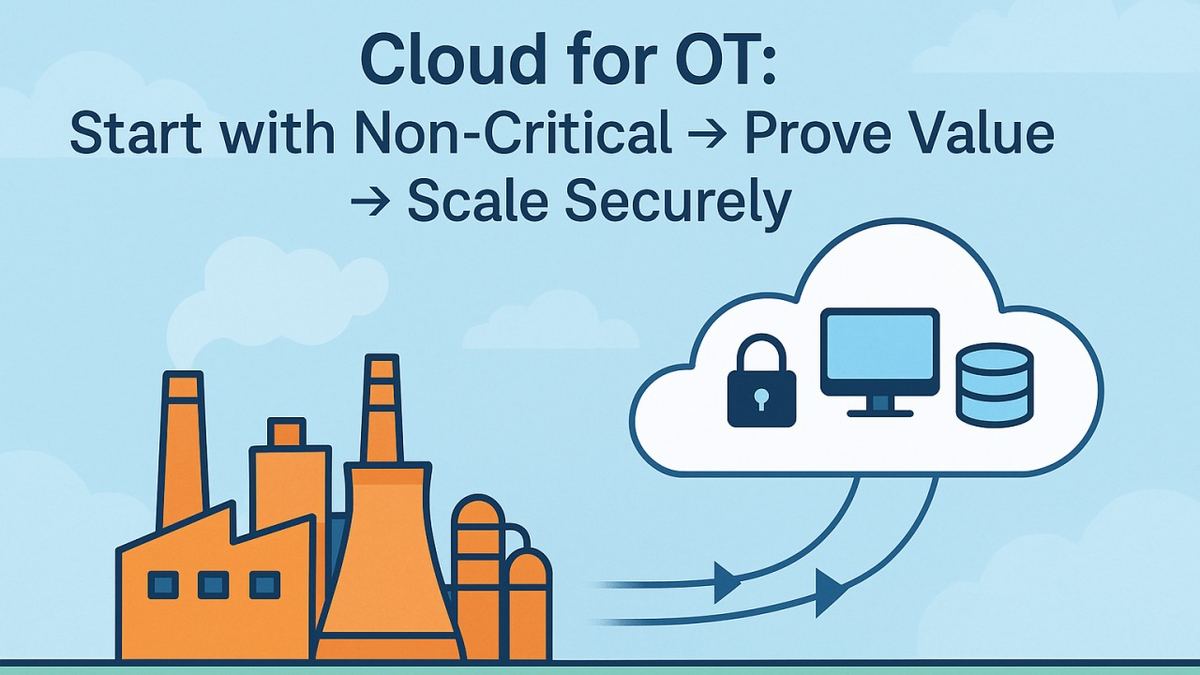
In my experience leading secure OT modernization, cloud in OT isn’t about lifting control loops to the internet—it’s about modernizing the supporting services around them. Start with non-critical OT services (patch orchestration, AV/EDR update infrastructure, file/ops servers, remote access gateways, asset telemetry/historian replication). Pilot at one site, measure, then scale.
Why now?
“Cloud connectivity offers a wealth of benefits for energy providers and other critical infrastructure operators.” — Owl Cyber Defense
But be clear-eyed:
“Simply put, moving industrial systems to the cloud renders traditional security concepts obsolete.” — David Masson, Darktrace
☁️ Hybrid patterns are the sweet spot for most plants:
“New developments in cloud, IoT, and edge computing have opened the door for traditionally on-premises OT workloads to evolve into hybrid workloads.” — AWS
Treat OT-to-cloud as a risk-engineered architecture, not a one-off integration: identity-first access, segmented paths, private endpoints, protocol-aware brokering/diodes, centralized monitoring, and clear ownership between IT and OT.
Start small. Prove value. Keep control-plane and safety-critical functions local while you mature controls and skills.
Your turn: If you were modernizing an OT environment, what would you pilot first—and which security control (e.g., private connectivity, JIT access, data diode) is non-negotiable on day one?
OTSecurity #ICS #CloudSecurity #IIoT #IndustrialCybersecurity #CriticalInfrastructure #ManufacturingSecurity #DigitalTransformation #EdgeComputing #CyberRisk #ITOT #OperationalTechnology #CyberAwareness #CloudAdoption #SecurityArchitecture #ZeroTrust #OTTransformation #CISO
Thanks to Eric May for collaborating with me on this!
Want help applying this in your environment?
Request a service